Browser fingerprinting is a tracking technique that uses information about your browser and device to recognize returning visitors without relying on traditional cookies. Websites or embedded scripts may combine details such as screen resolution, browser version, language settings, installed fonts, and graphics-rendering behavior to create a recognizable profile.
For example, deleting cookies may remove a stored tracking identifier, but some websites can still compare the technical characteristics your browser reveals during future visits. Fingerprinting is not always accurate or unique, and it can change as your software or device configuration changes.
This guide explains how browser fingerprinting works, which technical signals can be collected, how it differs from cookies, and what individuals and businesses can do to reduce privacy risks. It also covers legitimate security uses, potential regulatory obligations, and practical steps for reviewing fingerprinting behavior on a website.
What is Browser Fingerprinting?
A browser fingerprint is a collection of technical characteristics that a website can observe when your browser loads content or runs scripts. These details may include the operating system, browser configuration, screen dimensions, language preferences, and differences in graphics or font rendering.
Individually, these attributes may reveal little about a visitor. When combined, however, they can sometimes create a distinctive pattern that helps a website recognize a browser across visits. Fingerprints are not necessarily unique or permanent: multiple devices may share similar characteristics, and browser updates or configuration changes can affect recognition accuracy.
Browser fingerprinting has both legitimate and privacy-sensitive applications. Some services use device characteristics as one signal in fraud detection, account security, or abuse prevention. However, fingerprinting can also support advertising profiles and cross-site tracking when used to recognize visitors without relying on cookies.
Mozilla’s explanation of browser fingerprinting describes how device hardware, software, fonts, and browser settings can contribute to a recognizable profile. The privacy impact depends on which signals are collected, whether the information is linked to individuals, and how the resulting identifiers are used.
How Browser Fingerprinting Works Without Cookies
Cookies are stored on your device and are easy to delete or block. Fingerprinting relies on data your browser already exposes to render content and run code, so deleting cookies does not remove the underlying signals.
Fingerprinting techniques can collect information through browser APIs, font measurements, graphics rendering, and connection characteristics. Some techniques use values already available during normal page requests, while others actively run scripts to observe how the browser processes graphics, text, or audio.
Unlike cookie-based tracking, this process does not necessarily require storing a persistent identifier in the browser. However, fingerprint recognition can become less reliable when browsers reduce exposed information, standardize reported values, or block known tracking scripts. Websites may also combine fingerprints with cookies, login information, or other identifiers to improve recognition.
What Data Does Browser Fingerprinting Collect?
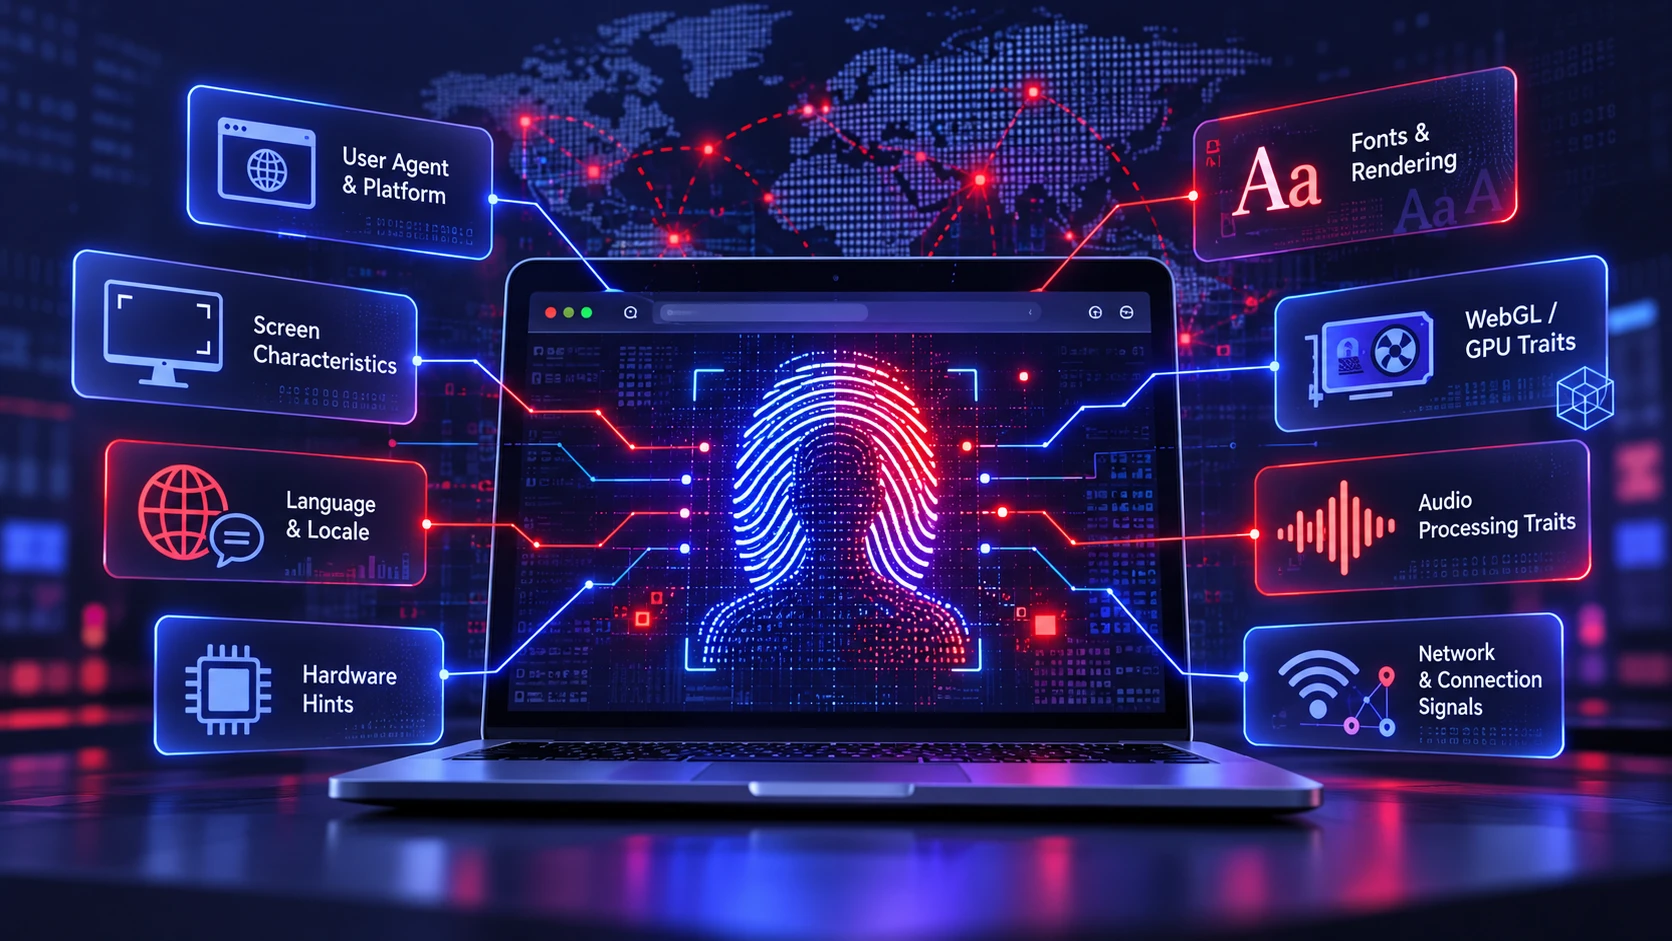
Fingerprinting is rarely one signal. It is a bundle of attributes collected at page load and during interaction to estimate uniqueness and stability.
- User agent and platform: Browser family, version, operating system, and device class.
- Screen and display characteristics: Resolution, color depth, pixel ratio, and available viewport size.
- Language and locale settings: Preferred languages, time zone, and region formats.
- Hardware hints: CPU cores, device memory buckets, and battery or power related APIs when available.
- Installed fonts and rendering differences: Text measurement results that change with fonts and system rendering.
- WebGL and GPU traits: Graphics vendor strings and subtle rendering output differences.
- Audio processing traits: Small differences in audio pipeline output used as a signal.
- Network and connection signals: IP address, TLS characteristics, and connection type hints.
Sites rarely need all of these. A few stable signals combined with a probabilistic model can be enough to recognize a returning device.
Common Browser Fingerprinting Techniques
Different techniques exist because browsers, extensions, and policies block some methods more than others. Trackers often combine several approaches to increase match rates.
Canvas and WebGL Fingerprinting
Canvas fingerprinting draws text or shapes and reads the rendered pixels. Slight differences in fonts, anti-aliasing, GPU, and drivers can produce a unique output.
WebGL adds more surface area by exposing graphics capabilities and rendering behavior. Even small variations can become a strong identifier when paired with other signals.
Audio Fingerprinting
Audio fingerprinting runs a short audio graph and reads the numerical output. Variations in hardware, drivers, and floating point behavior can create identifiable patterns.
This method is less visible to users because it runs quickly and does not require permissions in many setups. Modern browsers increasingly reduce access to high-entropy values, but it still appears in the wild.
Font and Text Measurement Fingerprinting
Font availability and rendering metrics can identify systems. Scripts measure how wide certain strings render and infer which fonts exist.
Even when direct font enumeration is restricted, indirect measurement can still leak useful information. Pairing this with screen characteristics can meaningfully narrow uniqueness.
TLS and Network-Level Fingerprinting
Some fingerprinting happens below the browser. TLS handshakes and connection behavior can be profiled to recognize clients, especially when combined with IP and routing patterns.
Network-level fingerprinting is different from browser-based techniques such as canvas or font fingerprinting. It can involve characteristics of network connections, TLS handshakes, or client software, and the information visible depends on where the observation takes place.
A VPN can change the IP address visible to destination websites and alter some network characteristics, but it does not automatically remove browser-level signals such as screen dimensions, fonts, or graphics behavior. Privacy protection therefore depends on the browser, network configuration, and tracking methods involved. No single tool guarantees that a user cannot be recognized across visits.
How Unique is a Browser Fingerprint?
Uniqueness depends on your device, browser, extensions, and how common your configuration is. A mainstream laptop with default settings tends to blend in more than a heavily customized setup with rare fonts and plugins.
Trackers also care about stability. Even if a fingerprint is not globally unique, it may be stable enough to link sessions on the same site or across a partner network.
Browser Fingerprinting vs Cookies: Key Differences
Cookies are explicit storage. Fingerprints are derived. Many tracking stacks use both along with server-side identifiers and login events to improve recognition.
| Tracking Method | How It Works | Stored on the Device? | Privacy Considerations | What Users Can Do |
|---|---|---|---|---|
| Browser Cookies | Stores small data values that browsers send with relevant requests | Yes | Can support login sessions, preferences, analytics, and tracking | Delete selected cookies, manage third-party cookie settings, and review site permissions |
| Local Storage | Stores website data accessible through supported browser APIs | Yes | Can preserve preferences or identifiers beyond a browsing session | Clear site data and review browser storage controls |
| Browser Fingerprinting | Combines browser and device characteristics to estimate a recognizable profile | Does not require a persistent client-side identifier | May support recognition even after cookies are deleted | Use browser fingerprinting protections and limit unnecessary tracking scripts |
| IP-Based Recognition | Uses network addresses and other connection information | Not necessarily | Shared or changing IP addresses can make recognition unreliable | Understand network privacy controls and VPN limitations |
| Account-Based or Server-Side Linking | Associates activity with logins, submitted identifiers, or backend records | Not necessarily | Can connect activity across sessions or devices | Review account privacy settings and limit unnecessary data sharing |
The comparison shows why clearing cookies does not necessarily prevent websites from recognizing returning visitors. Cookies store values in the browser, while fingerprinting relies on technical characteristics that may remain observable after cookie deletion.
For a deeper explanation of browser storage, read our guide to browser cache vs cookies, including what each stores and when to clear them. Privacy protection should consider both stored identifiers and other tracking techniques rather than relying only on occasional data deletion.
Browser Fingerprinting Privacy and Legal Risks
Browser fingerprinting may create legal obligations when it involves accessing information from a user’s device or processing information that identifies or can be linked to an individual. The UK’s Information Commissioner’s Office guidance on storage and access technologies identifies fingerprinting as one of the techniques that may fall within electronic privacy requirements.
The applicable rules depend on jurisdiction, purpose, implementation, and any relevant exemptions. Businesses should document which signals they collect, how those signals are used, who receives the information, and how long it is retained. Organizations using fingerprinting for advertising, analytics, or fraud prevention should assess the relevant privacy and consent requirements for their particular implementation rather than assuming that all fingerprinting is regulated identically.
For organizations, the risk is not only regulatory. Trust erosion, negative press, and partner scrutiny often follow unclear tracking practices, especially when fingerprinting is used for advertising or profiling.
How to Reduce Browser Fingerprinting and Tracking
No single browser setting can prevent every fingerprinting technique. However, privacy-focused browser features can reduce exposure by blocking known tracking scripts or limiting the technical details websites can collect.
Begin with your browser’s built-in tracking protection and keep the browser updated. Where supported, review fingerprinting-protection settings before installing additional extensions. Some strict privacy settings can affect website functionality, so choose protections that balance your privacy needs with compatibility. Focus on reducing unnecessary tracking rather than expecting complete anonymity.
- Use Built-In Fingerprinting Protection: Choose a browser that provides tracking and fingerprinting protections, and review its privacy settings. Mozilla’s Firefox fingerprinting protection guide explains how the browser blocks known fingerprinting scripts and limits some identifying information. Remember that protections vary by browser, configuration, and software version.
- Limit Extensions and Customizations: Install only browser extensions you need and review the permissions they request. Some extensions can introduce privacy risks, while unusual browser configurations may also contribute to fingerprint uniqueness. Our guide on whether browser extensions are safe explains how to assess permissions, developers, and data access before installing an add-on.
- Block third-party scripts: Reduce exposure by limiting third-party code where practical.
- Separate Browser Profiles: Use different profiles to organize work and personal accounts, cookies, and extensions. However, separate profiles do not automatically prevent fingerprint-based recognition when the same browser and device characteristics remain visible.
- Control permissions and site data: Restrict camera, microphone, and location access and clear site data regularly.
- Be cautious with VPNs: VPNs hide IP but do not remove device-level signals, so combine them with other protections.
A consistent browser configuration may help limit unnecessary identifying differences, but stronger privacy protection depends on the browser’s actual anti-tracking capabilities. Compare how different browsers handle fingerprinting, cookies, tracker blocking, and privacy settings before making a choice.
Our guide to the best internet browsers for privacy explores browser options and their privacy-related features. Keep in mind that browser protections can change with software updates, so review current settings and official documentation.
What Website Owners Should Know About Fingerprinting
Organizations may encounter fingerprinting through fraud-prevention platforms, analytics services, advertising scripts, and embedded third-party tools. Website owners should review which scripts are loaded, which browser characteristics they access, and whether collected information is shared with external vendors.
Browser privacy risks can also extend beyond traditional tracking scripts. Our article on AI browser privacy and security risks explains how AI-powered browsing features may introduce additional data access and sharing considerations. Businesses should evaluate each technology according to its actual data practices rather than assuming every tool operates in the same way.
Organizations should review the tracking technologies used across their websites, including analytics tags, fraud-prevention tools, embedded widgets, and third-party scripts. A technical and privacy review can help identify scripts that access device characteristics, determine which vendors receive information, and clarify how collected identifiers are used.
Website owners should document the purpose of each tracking tool, verify its privacy configuration, and seek appropriate technical or legal advice when necessary. Automated scans alone may not identify every fingerprinting technique, so combine testing with vendor documentation and implementation reviews.
How to Audit Browser Fingerprinting on a Website
A strong audit combines technical testing and documentation review. The goal is to learn which scripts access high-entropy APIs, what identifiers are created, and where data is sent.
- Inventory third-party resources: List all external scripts, pixels, SDKs, and embedded components loaded on key pages.
- Check for high-entropy API access: Look for usage of canvas, WebGL, audio APIs, font measurements, and detailed device properties.
- Review network calls: Identify endpoints receiving identifiers, hashed attributes, or unusual payloads tied to device characteristics.
- Validate consent and controls: Confirm tracking behavior matches user choices and that opt-out mechanisms truly reduce data collection.
- Document purpose and retention: Map each identifier to a purpose, retention period, and vendor responsibility.
Once you see what is happening in the browser and on the wire, decisions about removal, replacement, or configuration become much clearer.
Browser Fingerprinting Audit Checklist for Website Owners
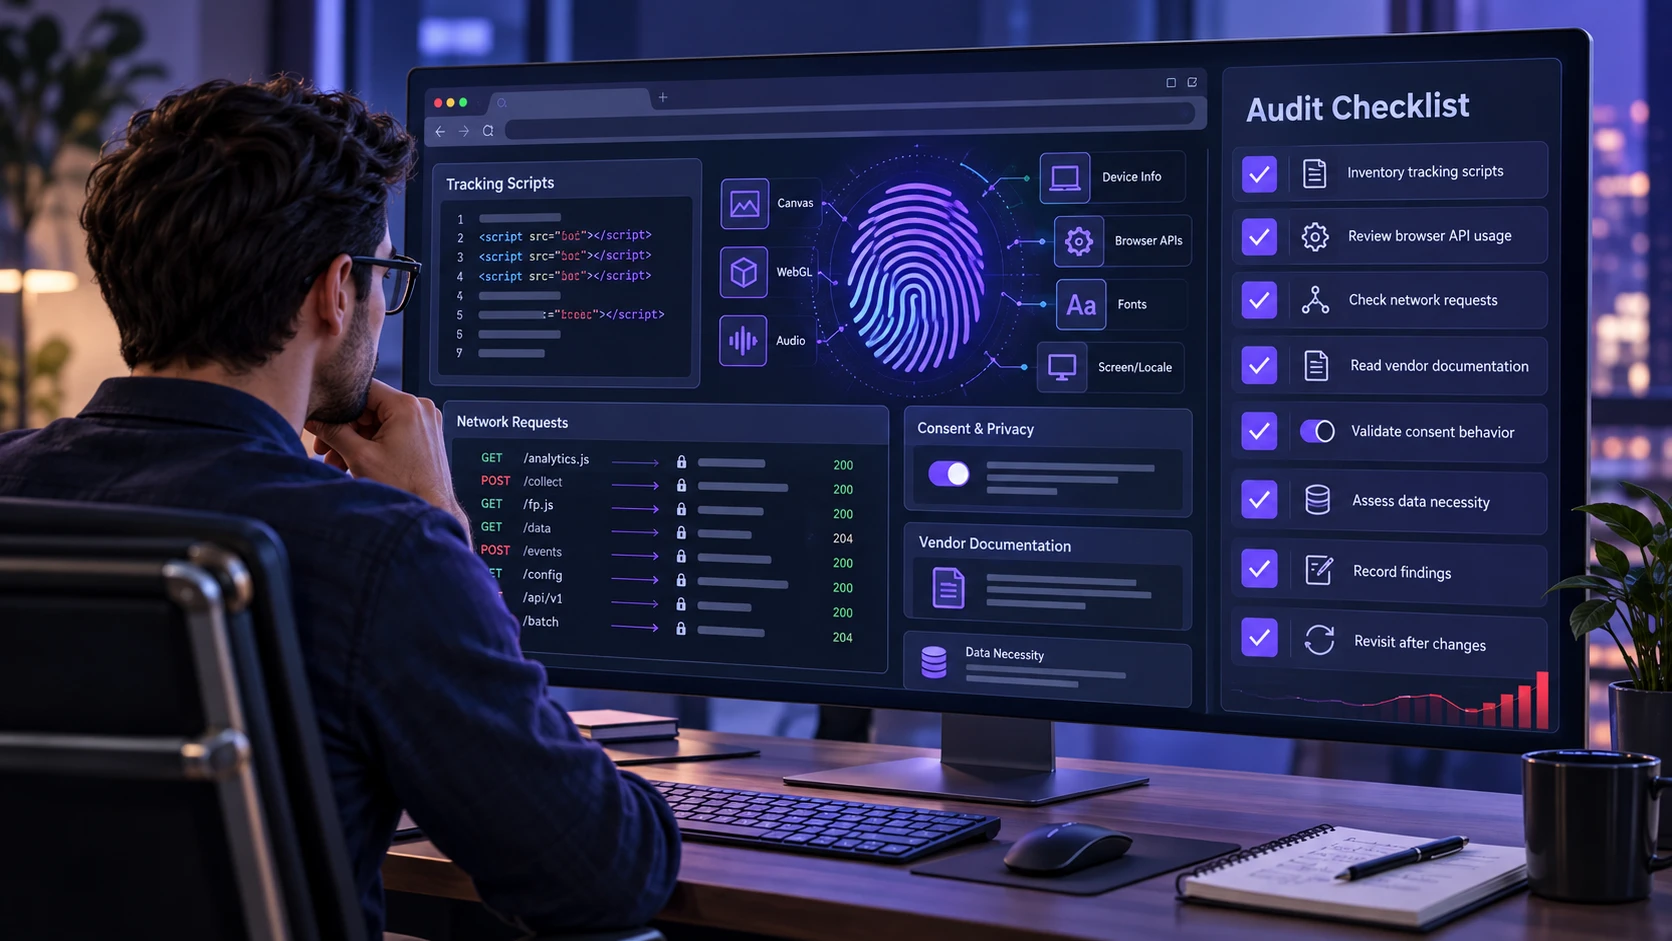
Website owners can use this checklist to investigate potentially invasive browser tracking and document what they find.
- Inventory Tracking Scripts: Identify analytics tags, advertising pixels, fraud-prevention tools, and third-party scripts loaded on important pages.
- Review Browser API Usage: Examine whether scripts access canvas, WebGL, audio processing, fonts, device information, or other detailed characteristics.
- Inspect Network Requests: Use browser developer tools to investigate where relevant scripts send information and whether identifiers appear in requests.
- Check Vendor Documentation: Review each provider’s stated data collection, processing purposes, sharing practices, and retention policies.
- Validate Consent Behavior: Test whether tracking-related scripts behave consistently with the user’s privacy choices and applicable legal requirements.
- Assess Data Necessity: Determine whether each collected characteristic is needed for security, website functionality, analytics, or another documented purpose.
- Record Findings: Document the script, vendor, observed behavior, associated risks, and any recommended changes.
- Review After Changes: Repeat relevant checks after adding advertising tags, updating plugins, or changing analytics and security tools.
Accessing browser characteristics does not automatically prove that a script is creating a tracking fingerprint. Confirm findings through technical investigation, documentation, and appropriate vendor communication.
Conclusion
Browser fingerprinting uses combinations of browser, device, and sometimes network characteristics to help recognize visitors without relying exclusively on cookies. Although fingerprinting can support fraud detection and account security, it can also enable tracking and profiling that users may not expect.
For individuals, browser tracking protection, careful extension management, and sensible privacy settings can reduce exposure, although no single tool guarantees anonymity. Deleting cookies alone does not remove the technical signals used for fingerprinting.
For businesses, responsible fingerprinting practices require a clear understanding of what information is collected, why it is needed, who receives it, and which privacy laws apply. Regular reviews of tracking scripts, vendors, and data-retention practices can help identify unnecessary collection and reduce privacy risks.
Frequently Asked Questions
Is Browser Fingerprinting Illegal?
Legality depends on jurisdiction, purpose, and how the data is used. When fingerprinting can identify or single out a user, it may be treated as personal data and require notice and consent. Organizations should also consider contractual duties and platform policies that restrict covert tracking.
Does Private Browsing Prevent Fingerprinting?
Private browsing mainly limits local storage such as cookies and history. It does not automatically block fingerprinting signals like screen size, rendering output, or device properties. It can still reduce linkability if it limits stored identifiers, but it is not a complete defense.
Does Blocking Cookies Prevent Cross-Site Tracking?
Blocking third-party cookies helps, but cross-site tracking can still happen through fingerprinting and server-side linking. Stronger protection usually requires a combination of tracker blocking, anti-fingerprinting features, and careful control of third-party scripts. Consistent settings across sessions matter more than occasional cleanups.
Does Using a VPN Prevent Browser Fingerprinting?
No. A VPN can change the IP address visible to websites, but it does not automatically hide browser characteristics such as screen resolution, fonts, graphics rendering, or device configuration. To reduce fingerprinting exposure, use appropriate browser anti-tracking protections alongside other privacy measures. A VPN alone does not guarantee anonymity.