Model Context Protocol (MCP) is an open standard for connecting AI applications to external tools, data sources and services through a consistent interface. It helps teams reduce one-off integrations while keeping context, permissions, and tool access more controlled. Anthropic originally introduced MCP in November 2024 as an open standard for connecting AI systems with external data and tools.
What Model Context Protocol MCP Means
MCP defines a common interface between an AI application and the tools it can use. Instead of hardcoding separate connectors for each vendor API, an app can talk to MCP servers that expose tools in a standardized structure.
At a high level, MCP separates the AI app that requests actions from the systems that carry out those actions. This makes tool access more modular and easier to govern.
Why MCP Exists and What Problem it Solves?
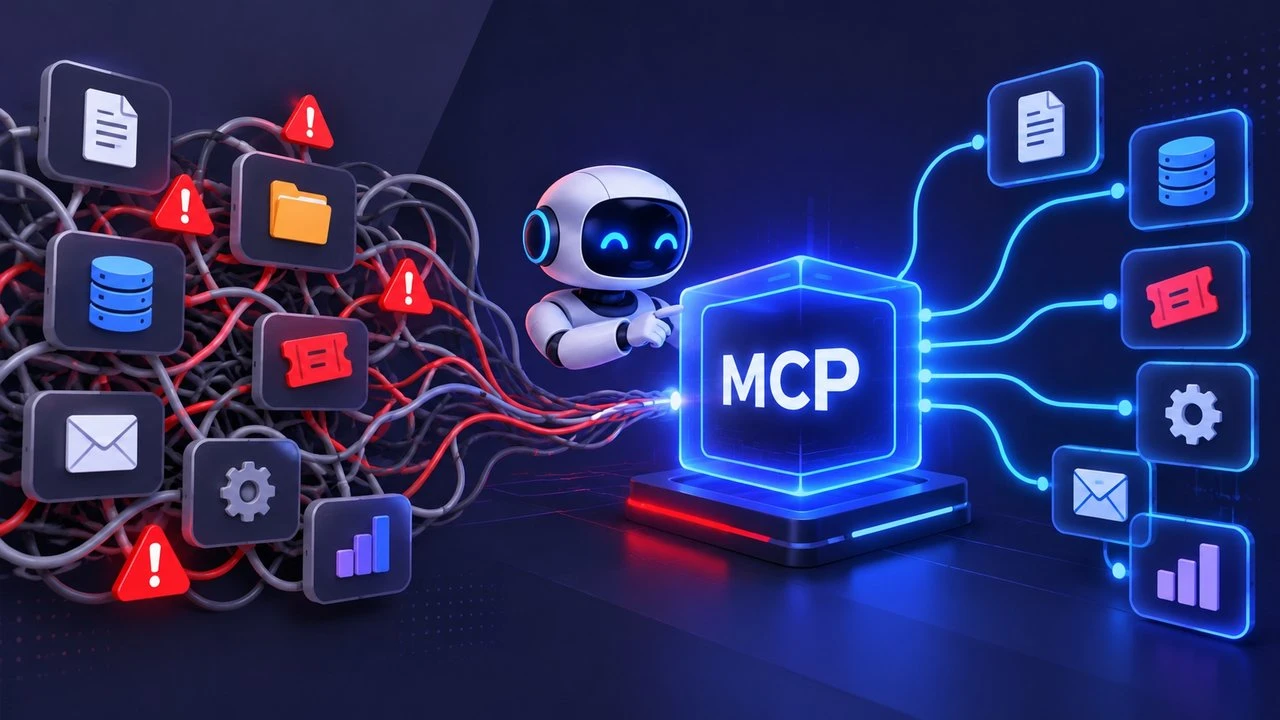
AI apps often need to search internal docs, read tickets, query databases, and trigger workflows. Without a shared protocol, each integration becomes custom work that is hard to secure, test, and maintain. This is part of the wider move toward AI agent protocols that standardize how agents, tools and systems communicate.
MCP addresses that fragmentation by standardizing how tools are described and invoked. It also supports safer patterns for handling sensitive data because tool access can be constrained at the server layer.
- Integration sprawl: Reduces the need to build and maintain many bespoke connectors.
- Inconsistent context: Encourages consistent payloads and tool schemas across systems.
- Security gaps: Centralizes permission checks and auditing where tools are exposed.
- Vendor lock-in risk: Makes it easier to swap tools or providers without rewriting core app logic.
These benefits show up most when an AI assistant has to operate across several internal systems.
How MCP Works at A High Level?
MCP uses a client-server architecture. An MCP host, such as an AI application or agent runtime, creates MCP clients that connect to one or more MCP servers. Each client maintains a connection with its corresponding server, while the servers expose tools, resources and other supported capabilities.
The key idea is that tools are presented with clear contracts. The AI app requests a tool call, the server validates and executes it, then returns structured results the model can use.
Core Building Blocks
- MCP Host: The AI application that coordinates MCP connections and the overall user experience.
- MCP Client: A component created by the host that maintains a connection with a particular MCP server.
- MCP Server: A program or service that provides capabilities and context to MCP clients.
- MCP Tools: Executable functions that allow AI applications to perform actions such as querying APIs or databases.
- Resources: Data sources that provide contextual information such as files, records or API responses.
- Prompts: Reusable templates that help structure interactions with language models.
With these pieces, teams can standardize tool calling, reduce duplicated work, and keep behavior predictable.
MCP Compared With Traditional Integrations
Traditional integrations tie an AI app directly to each external API. That approach works, but it tends to produce repeated logic for authentication, schema mapping, error handling, and rate limits.
With MCP, an AI application can use a common protocol interface to work with multiple compatible MCP servers instead of implementing a completely different interaction pattern for every integration. That creates a cleaner boundary between the model layer and system-of-record integrations.
| Approach | What Gets Built | Operational Impact |
|---|---|---|
| Direct API Integrations | Custom connector per tool with separate schemas | Higher maintenance and inconsistent behavior |
| MCP With Shared Servers | Standard protocol plus servers that expose tools | More reusable integrations and easier governance |
| Plugin Style Tooling | App-specific plugin contracts and packaging | Portability depends on vendor and runtime |
| Middleware Abstraction Layer | Custom internal framework for auth and mapping | Works well but can become a platform to maintain |
The right choice depends on scale, security needs, and how many systems the AI app must touch.
Security and Governance Considerations

MCP can improve security when implemented with strong controls. The server boundary creates a natural place to enforce permissions, validate inputs, and limit what the AI app can request. MCP itself does not automatically make tool access secure; applications and servers still need appropriate authorization, least-privilege access and human approval for sensitive actions.
Tool access should be treated like any other production integration. It needs authentication, authorization, logging, and clear data handling rules. Many of the same principles also apply to API security, particularly authentication, authorization, input validation and rate limiting. Teams should also follow established AI agent security best practices when tools can access sensitive systems or perform actions.
Practical Controls To Apply
- Least privilege: Expose only the actions the AI app truly needs and scope them by role.
- Input validation: Reject unsafe or malformed tool calls before they reach systems of record.
- Audit logging: Capture who initiated the request, what tool ran, and what data was accessed.
- Rate limiting: Prevent runaway calls and protect downstream services.
- Data minimization: Return only what is required for the model to proceed.
These practices reduce risk while keeping tool-enabled AI useful in real operations.
Where MCP Fits in Modern AI App Architecture
MCP is most valuable in AI assistants, agentic workflows, and internal copilots that need consistent access to enterprise tools. It also fits well when multiple AI apps need to share the same connectors.
It can sit alongside retrieval augmented generation, vector search, and orchestration layers. MCP focuses on the interface for tools and context rather than on model selection or prompt design. The broader process of deciding what context, constraints, sources and tools a model should receive is often described as context engineering.
Common Tool Categories Exposed Through MCP
- Knowledge retrieval: Document search, wiki access, and policy lookups with controlled context.
- Operational actions: Ticket creation, status updates, and approvals with guardrails.
- Data access: Querying analytics stores or databases with parameterized queries.
- Communication: Drafting messages, creating summaries, and posting updates where allowed.
As the number of tools grows, a protocol-based approach helps keep the system manageable.
Implementation Guidance for Teams
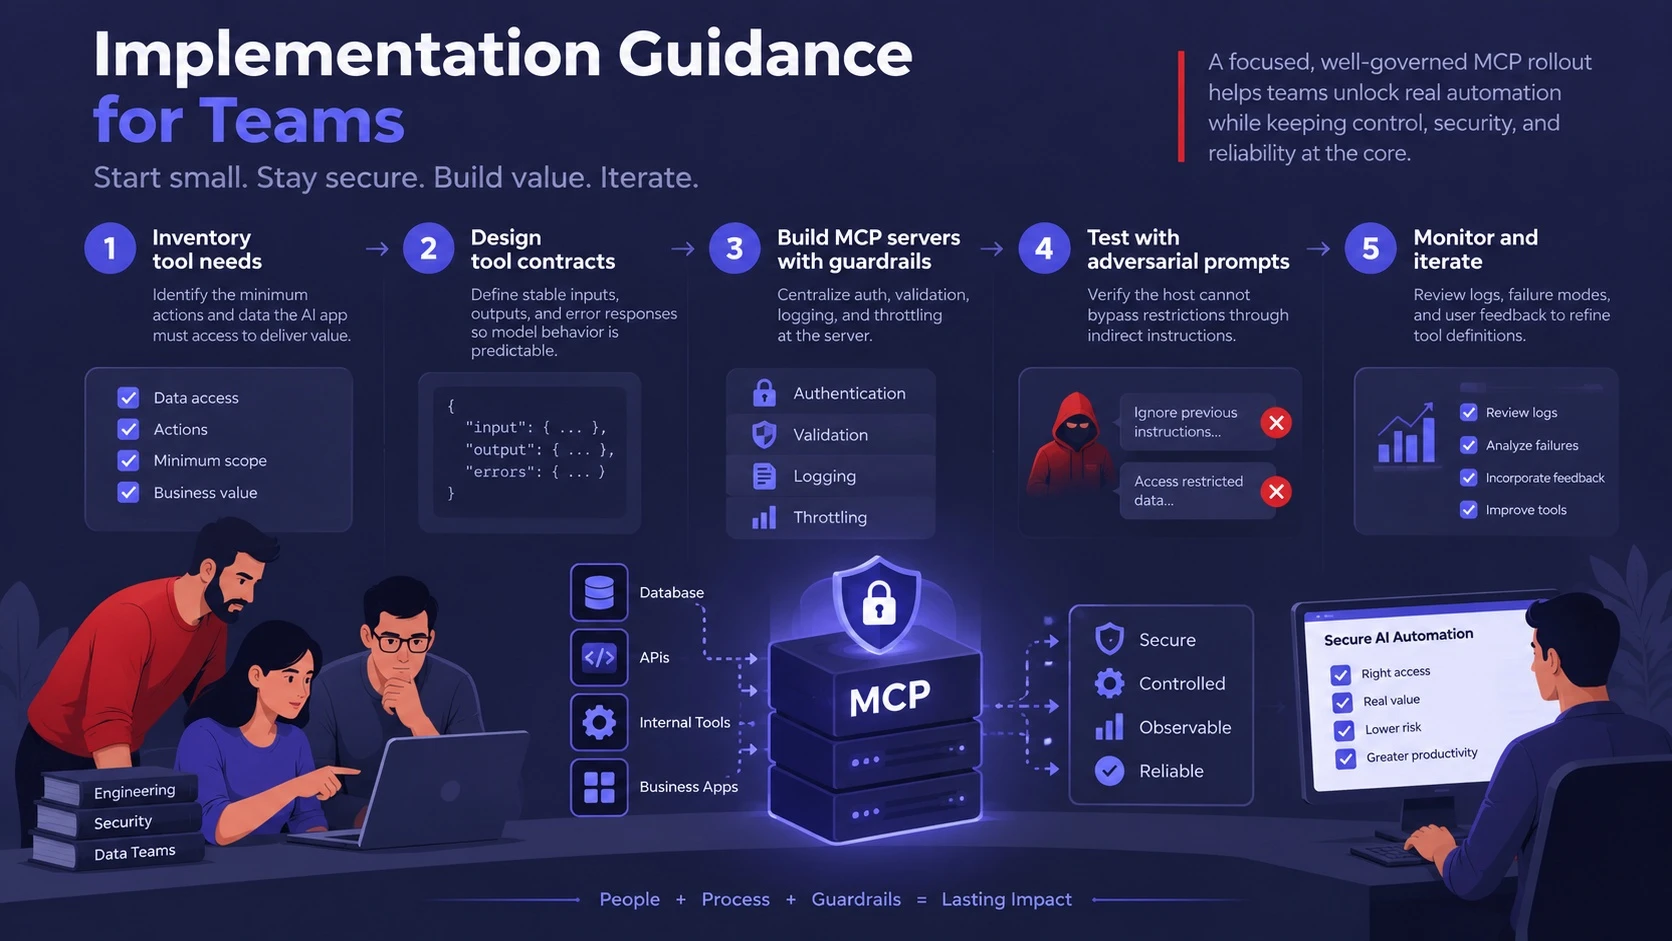
A clean MCP rollout starts with a small set of high-value tools and tight permissions. It is better to launch a narrow but reliable set of capabilities than a wide surface area that is hard to govern.
Organizations also need alignment between engineering, security, and the teams that own the data sources. Clear ownership prevents integration drift and access creep.
- Inventory tool needs: Identify the minimum actions and data the AI app must access to deliver value.
- Design tool contracts: Define stable inputs, outputs, and error responses so model behavior is predictable.
- Build MCP servers with guardrails: Centralize auth, validation, logging, and throttling at the server.
- Test against prompt injection and adversarial instructions: Verify that untrusted content cannot make the host or agent bypass tool restrictions.
- Monitor and iterate: Review logs, failure modes, and user feedback to refine tool definitions.
This approach keeps the integration surface controlled while still enabling useful automation.
How TechBonafide Can Help With MCP-Ready AI Integrations
Teams often need help turning a promising AI prototype into a governed, production-ready system. TechBonafide typically focuses on practical AI engineering patterns such as reliable tool calling, integration architecture, and secure deployment workflows.
If you are evaluating MCP, it helps to treat it as part of a broader AI application stack. A structured build plan that covers data access, identity, monitoring, and model behavior testing can reduce rework and speed up adoption.
Conclusion
Model Context Protocol (MCP) is a structured way for AI apps to connect to tools and data sources without rebuilding integrations repeatedly. It provides clearer boundaries, more consistent tool contracts, and better places to enforce security controls.
When implemented with least privilege, validation, and observability, MCP can support scalable AI assistants that remain maintainable as systems and requirements evolve.
Frequently Asked Questions
Is MCP Only For Large Enterprises?
No. Smaller teams benefit when they need to connect an AI assistant to several tools and want consistent interfaces. The value increases as the number of integrations and stakeholders grows.
Does MCP Replace Retrieval Augmented Generation?
No. Retrieval augmented generation focuses on bringing relevant knowledge into the model context for better answers. MCP focuses on how the AI app connects to tools and resources through standardized contracts.
What Should Be The First MCP Server A Team Builds?
Start with a server that exposes a small number of high-value, low-risk read-only tools such as document search or policy lookup. Once behavior is stable and auditing is solid, add narrowly scoped write actions with approvals where needed.